Database rules switched off
Tables anyone can read, or change, with the public key every app ships with.
✓Access rules on every table, tested from the outside.
Security · fixes · private AI
For founders and companies building with Lovable, Bolt, Cursor or Replit. And for offices that want AI without sending client files out. One engineer, from the first check to the fix.
No code or passwords to start · reply within one working day
What I solve
It works. But can a stranger read your users' emails, messages and photos with one request? Often, yes.
✓I test it like an attacker, close every door, and show you the proof.
Check my app → CompaniesSales, finance and ops ship their own apps in an afternoon. Nobody checked who else can open them.
✓I find every AI-built tool, test what's exposed, and lock it down without stopping the team.
Check our tools → OfficesYour staff already paste contracts and records into free AI chats — onto servers you don't control.
✓AI on a machine in your office: same help, nothing leaves, every answer shows its source.
See private AI →Also:My AI-built app is stuck at 80%My agency holds my app's keysMy device needs an appI'm a coach and want my own app
How it happens
Built in a weekend with an AI tool. Sign-up, payments, chat — it all works. Nobody asks who else can read the database.
They upload photos, type their home address, send messages they'd never post in public.
No password, no hacking tool. The database answers anyone who asks — because the access rules were never switched on.
“We're writing to tell you your personal data was exposed…” In the EU you have 72 hours to report it to the regulator.
I find the open door first, close it, and send you the request that proves it's shut.
What I check, then fix
Tables anyone can read, or change, with the public key every app ships with.
✓Access rules on every table, tested from the outside.
Payment, email or AI keys anyone can pull out and run up your bill with.
✓Keys moved to the server; the old ones replaced.
The screen hides other people's data. The server still hands it out.
✓Every request checks who is asking.
Uploaded photos, IDs and documents open to anyone with the link.
✓Private storage with links that expire.
Who does the work
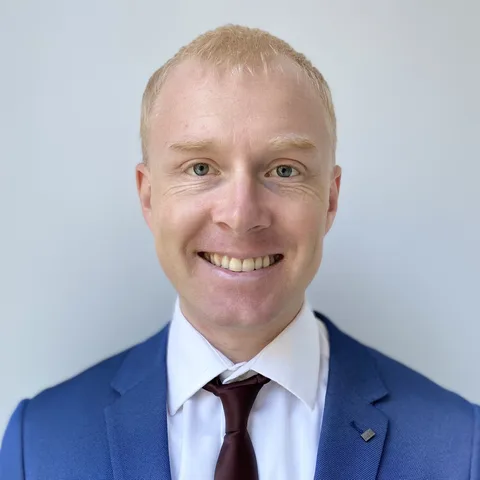
I'm Oleksii Mykhalchuk. Thirteen years as an electrical and automation engineer — nine of them on ships: radars, satellite links, networks and automation. At sea there's nowhere to send a broken board. You find the fault and fix it, now.
Now I build and run iOS, Android, web and backend apps alone — with real users and real data. I check your app the way I check my own.
13 yrsengineering
9 yrsat sea
4platforms shipped solo
5languages
How it works
Your app, tool or website, and what you built it with. No passwords, no code needed to start.
From the outside, the way someone would who wants your data: the database, keys, logins and files.
What's open, how bad it is, and the request that proved it. I fix it, or your developer does — then I test again.
No obligation. I read every message myself and reply within one working day.
Questions
Not to start. The first look is from the outside, the way an attacker would see your app. For fixes you add me to the project, and remove me when we're done.
What's open, how bad it is, and the exact request that proved it — in plain words. If your app is clean, I tell you that too.
Yes. I fix it myself, or give your developer the exact list, and then test again so you know the doors are shut.
Yes. If people on your team build tools with Lovable, Replit, Cursor or similar on company data, I find those tools, test what they expose and lock them down — without stopping the team from building.
No. What I find stays between us, and I delete any data I happen to see.
Yes — iOS, Android, web and backend, including apps that talk to devices over Bluetooth or Modbus, and AI that runs on your own hardware.
Trogir, Croatia. I work remotely in English with clients across Europe and North America.
Writing
Since iOS 26 on iPhone and Gemini Nano on Android, an app can run a language model on the user's own phone with no per-request API cost — but only on recent flagship devices, so most apps still need a cloud fallback.
The iPhone Duo opens to 7.6 inches and reaches customers on 23 October. If your app assumed one screen that never changes shape, that assumption now has a delivery date attached.